A recently reported security issue affects NexoPOS 6.2.4 and earlier. At the same time, the PHP project has disclosed two critical vulnerabilities affecting commonly deployed PHP versions. If you manage your own NexoPOS installation, update both NexoPOS and the PHP runtime on your server as soon as possible.
Action required
The NexoPOS vulnerability
The reported NexoPOS issue concerns authorization around the database-migration process. Database migrations are trusted operations used during an update to modify an installation's database structure.
On affected versions, migration execution was not restricted as tightly as intended. Under certain conditions, this could allow migration operations to be triggered outside the normal update workflow.
Depending on the installation and server configuration, the potential consequences include:
- Unauthorized database changes
- Damage to data integrity
- Application errors or interrupted operations
- Temporary loss of access to the point-of-sale system
- Additional exposure through an improperly controlled update process
We are intentionally not publishing technical details that could make exploitation easier. The vulnerability affects NexoPOS 6.2.4 and earlier.
The fix is available
NexoPOS 6.3.0 is the recommended solution.
NexoPOS 6.3.0 restricts migration execution to valid migrations that are actually pending, validates migration paths, and prevents migration files from being loaded outside their intended directories.
The release also introduces:
- More granular POS permissions
- Order-level access controls
- Stronger API-token authorization
- Capability-based authorization for AI and MCP features
- A hardened My NexoPOS connection process
- Reporting, localization, label-printing, and reliability improvements
Customers who cannot move to NexoPOS 6.3.0 immediately should install the NexoPOS 6.2.5 security patch as a temporary measure. Moving to the latest stable release remains the recommended path.
PHP must also be updated
Updating NexoPOS alone is not sufficient if the server is still running a vulnerable PHP version.
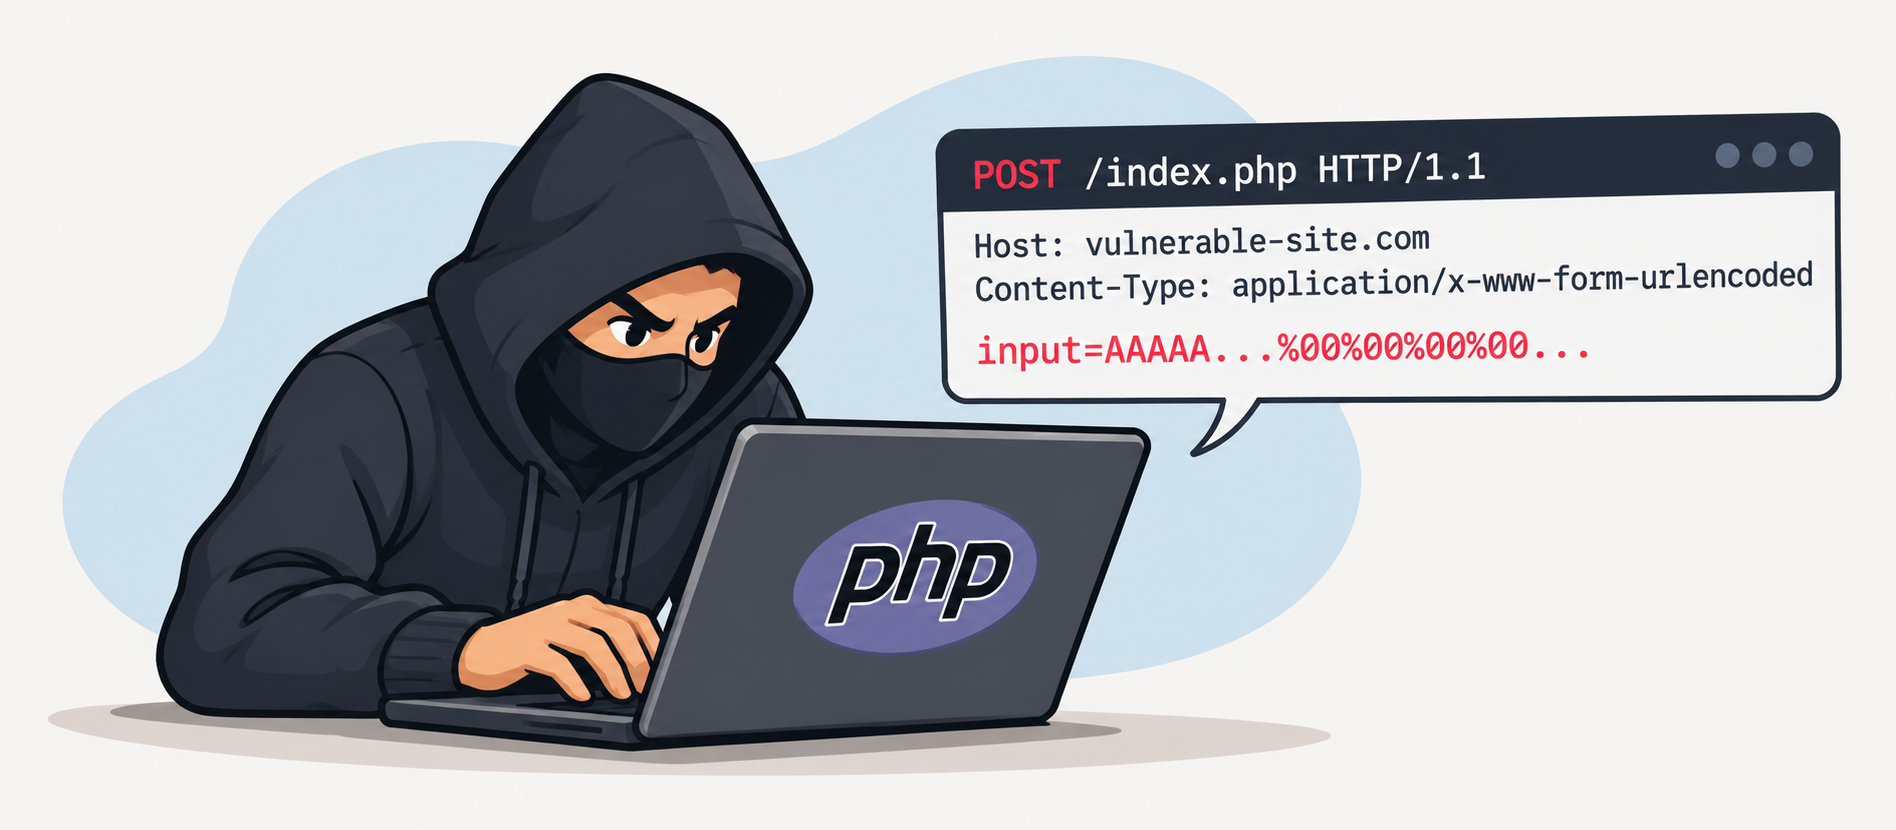
On 21 October 2026, the PHP security team disclosed two critical vulnerabilities, both rated CVSS 9.2 Critical:
- CVE-2026-109618: remote code execution through out-of-memory corruption
- CVE-2026-109619: remote code execution through stale global state
These vulnerabilities can allow unauthenticated remote code execution on PHP installations serving web requests. The PHP project considers installations using PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, and LiteSpeed to be at risk.
Administrators should update to at least one of the following secure versions:
- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12
PHP 8.1 and earlier no longer receive regular security updates from the PHP project. Installations using these versions should move to a supported PHP branch or obtain a verified patched package from their operating-system or long-term-support vendor.
Updating PHP is required
Read the official PHP security advisory.
What self-hosted customers should do
Before making any changes, back up your NexoPOS database and application files. Then:
- Ask your hosting provider or server administrator to update PHP to a secure version.
- Restart PHP-FPM, Apache, or the relevant web workers after updating PHP.
- Upgrade NexoPOS to version 6.3.0.
- Run pending database migrations through the normal NexoPOS update process.
- Confirm the installed NexoPOS and PHP versions.
- Review and test custom modules, integrations, and themes.
If your installation already runs NexoPOS 6.2.5 or 6.3.0, the NexoPOS migration fix is included. You must still verify that the underlying PHP runtime has been updated.
Prefer not to manage server security yourself?
Running a self-hosted point-of-sale system means maintaining more than the application. You must monitor PHP, the web server, database services, operating-system packages, backups, and security updates.
NexoPOS Cloud removes much of that operational burden.
NexoPOS Cloud customers do not need to perform the manual application and server-update process described above. Platform maintenance and security updates are handled behind the scenes, allowing customers to focus on running their businesses instead of maintaining hosting infrastructure.
If you would prefer a managed NexoPOS environment with updates handled for you, now is a good time to migrate.
Security updates should not be postponed. Whether you remain self-hosted or move to NexoPOS Cloud, make sure your business is running on a maintained and fully patched platform.